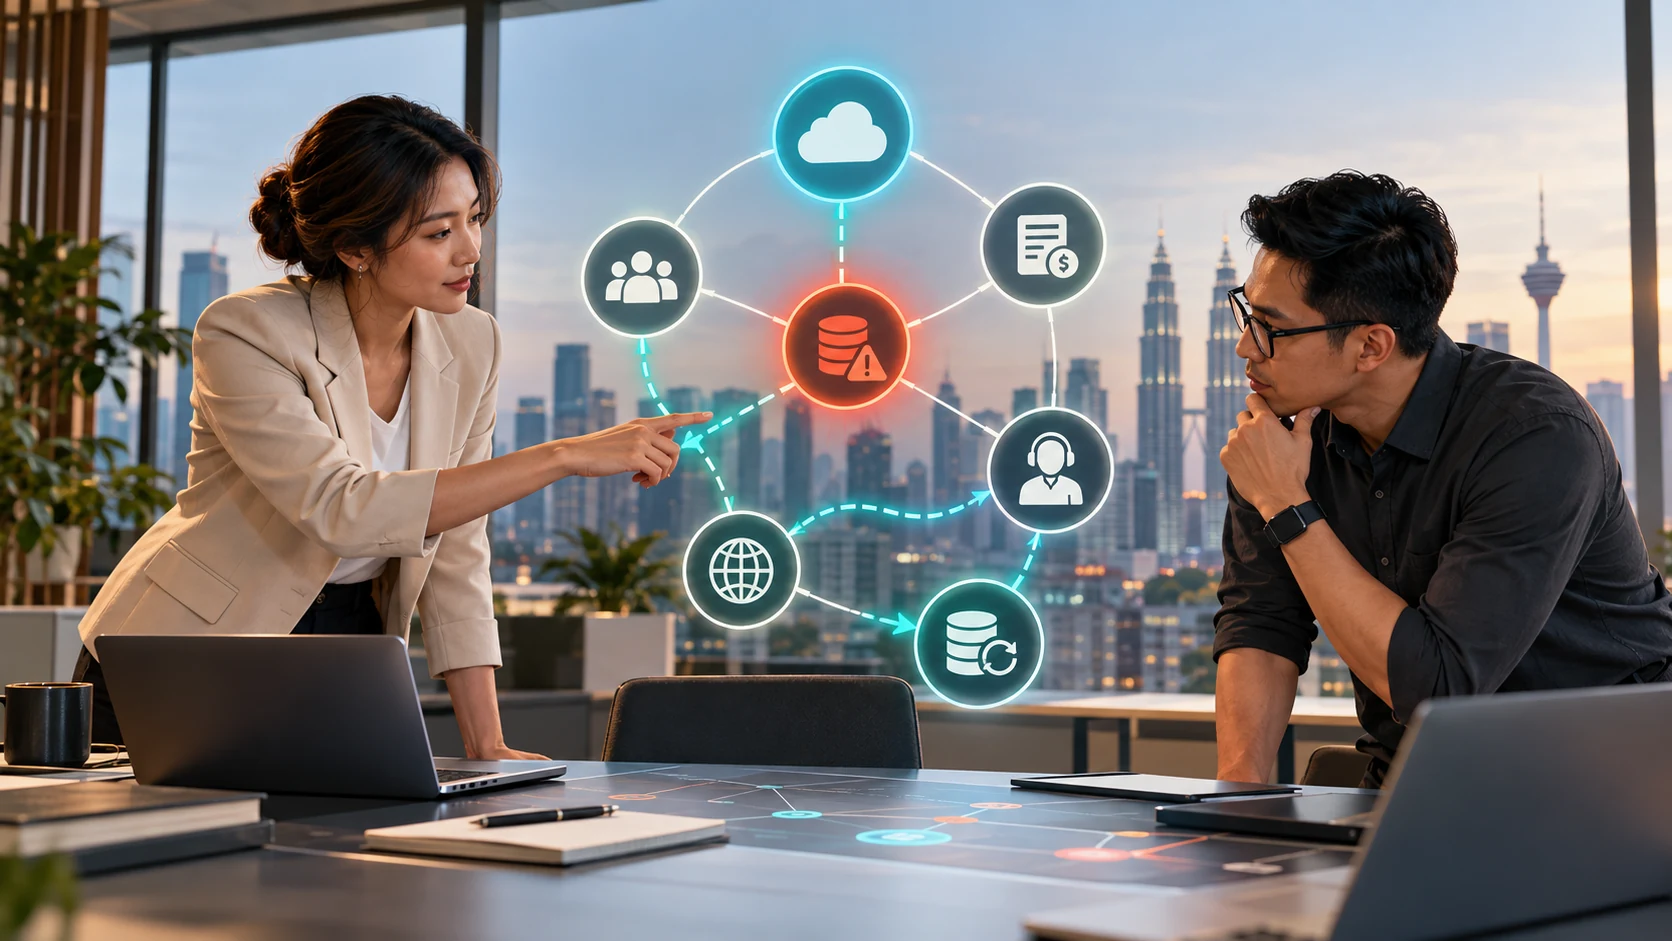
Your payroll system, Microsoft 365 tenant, accounting platform, domain registrar, backup service and IT support tools may sit outside your office. The business impact does not. If one provider is breached, locked out or unavailable, your company may lose access to email, invoices, customer records or recovery systems without a single attacker touching the office firewall.
This is why third-party cyber risk is no longer a procurement formality. ENISA’s Threat Landscape 2026, published on 22 September, says that cyber dependencies are expanding the attack surface and that supply-chain and third-party attacks can produce large-scale or highly disruptive incidents. Its evidence covers the European Union, not Malaysia, so the figures should not be treated as Malaysian statistics. The operating lesson, however, travels well: a connected service can become part of your incident even when somebody else runs it.
1. Map the services that can stop the business
Do not begin with a hundred-question supplier questionnaire. Start with the ten external services whose loss would interrupt revenue, payroll, customer delivery, compliance or recovery. For each service, record the provider, business owner, technical owner, information handled, administrative login, renewal date and maximum tolerable outage.
Then add the hidden dependencies. Does the payroll portal rely on one employee’s email for password resets? Does the backup platform use the same identity provider as production? Is the company domain registered through a former web developer? A simple dependency map often reveals that several “separate” services share one login, one reseller or one support contact.
2. Ask for evidence, not a promise of security
NIST’s July 2026 Due Diligence Assessment Quick-Start Guide describes supplier due diligence as research that helps an organisation make informed decisions about new and existing ICT suppliers. For an SME, the questions can remain practical:
- Which security practices protect privileged access, and is multifactor authentication enforced?
- How quickly will the supplier notify you of a suspected incident or material service disruption?
- What logs, audit records or investigation support will be available?
- How is your data backed up, restored, exported and securely removed at contract end?
- Which subcontractors or upstream services are required to deliver the service?
A sales presentation is not evidence. Depending on the risk, useful evidence may include a current independent assurance report, penetration-test summary, documented restore result, incident-notification clause or a clear shared-responsibility statement. The goal is not to collect documents for their own sake; it is to find gaps before an emergency.
3. Find concentration risk
A supplier can be secure and still be a single point of failure. Look for several critical services using the same identity platform, internet link, DNS provider, cloud region, remote-management tool or backup administrator. Also check whether the same MSP account can reach every customer system.
ENISA’s report highlights how attacks spread across interconnected digital services and infrastructure. That does not mean every SME needs multiple providers for everything. It means management should consciously accept or reduce concentration risk. A secondary internet path, offline recovery contact, separate emergency administrator or independent backup copy may be more valuable than another security dashboard.
4. Test recovery and exit before you need them
Ask the supplier to demonstrate a realistic recovery step: restore a representative file, export a customer list, recover an administrator account or produce an audit trail. Record who can authorise the action and how long it actually takes. “Backups are enabled” is not the same as “we can restore operations within the required time.”
Exit readiness matters too. Confirm the format of exported data, the notice period, transition assistance, credential revocation and deletion confirmation. If the contract ended tomorrow, could a new provider operate the environment without relying on the old provider’s account?
5. Run a 45-minute dependency incident exercise
Choose one scenario and walk through it with management, IT and the service owner. For example: the company’s cloud accounting provider reports suspicious access and temporarily disables sign-in. Who confirms the notice is genuine? Can invoices still be issued? Where is the latest usable export? Who speaks to customers, Finance and the board? What evidence must be preserved?
Hypothetical example: A 50-person Malaysian distributor uses one Microsoft 365 account to administer its domain registrar, cloud backup and online sales platform. A compromised administrator session leads to emergency suspension of the account. Production data is not necessarily stolen, but the company cannot change DNS or start a restore. The immediate improvement is not another product: it is separate named administrators, protected emergency access, tested recovery contacts and documented ownership. This is an illustrative scenario, not an AXO client incident.
After the exercise, assign each gap an owner and due date. The board-level summary can fit on one page: critical dependencies, unacceptable single points of failure, recovery evidence, contractual gaps and the next test date.
Third-party risk management does not require an enterprise-sized governance team. It requires knowing which suppliers can stop the business, verifying the controls that matter and keeping a workable route back to operations. If your dependency map has never been tested, begin with the five services you would least want to lose on a Monday morning.
For help reviewing your cloud, application and managed-service dependencies, contact AXO Technologies at axotechnologies.com/contact-us/.
Sources
- ENISA, ENISA Threat Landscape 2026, published 22 September 2026.
- ENISA, How dependencies weaken our digital resilience, press release, 22 September 2026.
- NIST, Cybersecurity Supply Chain Management: Due Diligence Assessment Quick-Start Guide (SP 1326), published 8 July 2026.
- NIST, Cybersecurity Framework 2.0: Quick-Start Guide for Cybersecurity Supply Chain Risk Management (SP 1305), published 21 October 2024.
- CISA, Operationalizing Vendor Supply Chain Risk Management Template for SMBs, accessed 12 October 2026.